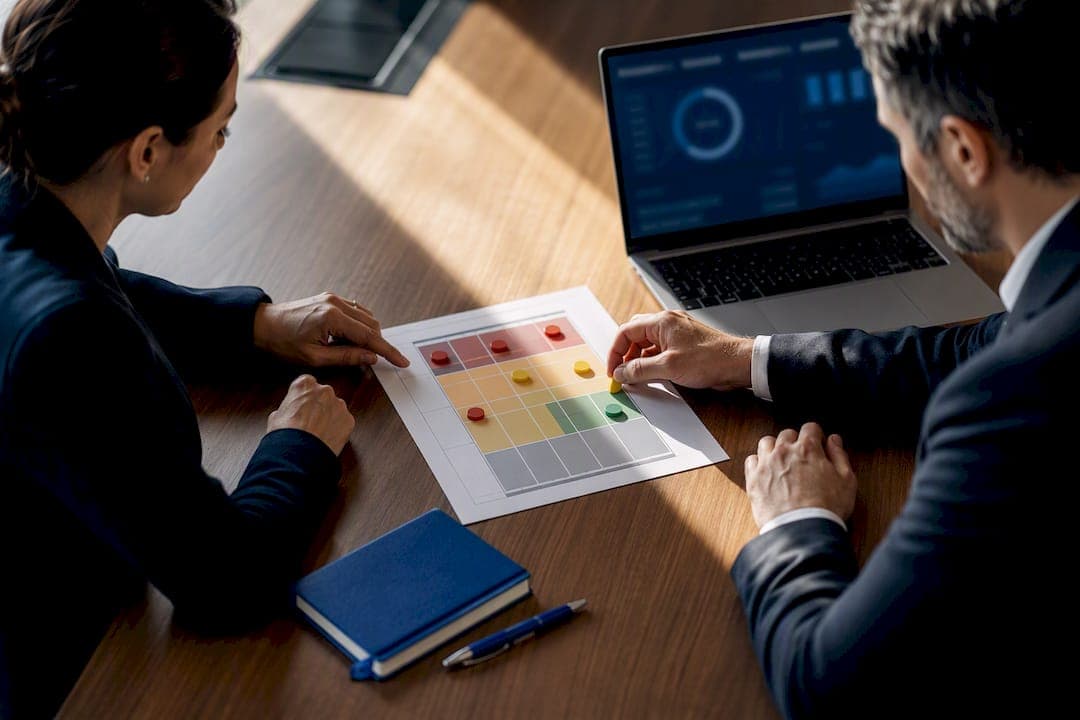
An IT risk register is a structured record of your organization's material technology and cybersecurity risks, written in business terms so leadership can act on them. The first step is simple: list your top enterprise-impacting IT risks, assign a named owner to each, and record a treatment decision. This structure follows the guidance in NIST IR 8286.
TL;DR:
- Risks that could materially impact the organization should be prioritized, with inherent and residual scores used to assess their severity.
- Every risk entry requires a clear business-impact description, a named owner, and a documented treatment decision to ensure accountability and clarity.
- Consistent scoring, categorization, and linking to asset inventory enable effective aggregation of risks into an enterprise-wide profile.
- Regular review cycles, at least quarterly, are essential to keep risk scores accurate and prevent the register from becoming outdated or unmanageable.
- Linking incident analysis to the risk register aids in updating scores and controls, reducing the likelihood of overlooked exposures.
Table of Contents
- Fields to include in a practical IT risk register
- Step-by-step process to create and run the register
- Scoring and prioritization: choosing scales and rolling up to ERM
- Notional examples: sample register rows to copy and adapt
- Governance and maintenance: ownership, approvals, and change control
- Secure Techies case study: a real-world register in practice
- Integration with asset inventory and configuration management
- Linking incidents and root cause analysis to risk updates
- Common pitfalls in maintaining an IT risk register
- What the register actually needs to work
- How Secure Techies can help you build and maintain a register
- Sources
- FAQ
Fields to include in a practical IT risk register
A usable register needs consistent fields so entries can be compared, scored, and rolled up into enterprise reporting. NIST IR 8286's notional template calls for a description, impact, likelihood, mitigation strategy, owner, and ranking, and most working registers expand on that core set to support day-to-day tracking.
At minimum, include these fields for every entry:
- ID and title: a short reference code and a plain-language name for the risk.
- Business-impact description: what happens to revenue, operations, or reputation if the risk materializes, written for a non-technical reader.
- Asset(s) affected: the systems, applications, or data sets tied to the risk.
- Threat and vulnerability summary: the specific weakness and what could exploit it.
- Risk category: for example access control, third party, data loss, or infrastructure.
- Inherent likelihood, impact, and score: the risk level before any controls are applied.
- Existing controls: what is already in place to reduce likelihood or impact.
- Residual likelihood, impact, and score: the risk level after current controls.
- Treatment decision: mitigate, transfer, accept, or avoid.
- Named owner and approver: who manages the risk and who signed off on the decision.
- Status and review date: current state and the next scheduled check-in.
- Evidence links and control references: supporting documentation and mapped control IDs.
Writing the description in business language matters because a board or executive team rarely responds to "unpatched CVE on a legacy server." They respond to "a legacy billing server outage could halt invoicing for up to three days." When residual risk still exceeds appetite, note a target residual score and a date for re-measurement, and record how control effectiveness was verified rather than assumed, following guidance on how to define, measure, and apply risk appetite.
Step-by-step process to create and run the register
Building the register is a one-time exercise. Running it is a recurring process, and NIST SP 800-30 frames that process in four stages: prepare, conduct, communicate, and maintain. Applied to an IT risk register, that becomes a repeatable sequence your team can follow every cycle.
- Establish context and scope. Decide which systems, business units, or projects the register covers, and confirm this with the risk office or IT leadership.
- Identify risks. Pull candidates from vulnerability scans, audits, incident history, vendor reviews, and staff input.
- Record entries. Log each risk in the template using consistent field definitions.
- Assess likelihood and impact. Use NIST SP 800-30 methods to estimate both inherent and residual values.
- Calculate exposure and prioritize. Score each risk and rank the list so the most material items surface first.
- Assign owners and treatment decisions. Every entry needs a named owner and a documented choice: mitigate, transfer, accept, or avoid.
- Track remediation activity. Log actions, target dates, and status updates against each open risk.
- Report to leadership. Summarize top risks, changes since the last cycle, and any items exceeding risk appetite.
- Perform scheduled reviews. Revisit the full register on a set cadence and refresh scores as conditions change.
Security and IT staff typically drive identification and assessment, business owners confirm impact and sign off on treatment, and a risk office or compliance lead oversees reporting and cadence. Each step should produce an artifact: a risk detail record, a control mapping, or an evidence folder that supports the score.
Pro Tip: Keep a one-page "top ten" extract of the full register for executive meetings; it forces prioritization and keeps leadership focused on what actually needs a decision.
Scoring and prioritization: choosing scales and rolling up to ERM
A 5x5 likelihood by impact matrix is the most common scoring approach, and it works well because it is simple enough for business owners to use without training. Ordinal scales (low, moderate, high, critical) are easier to apply consistently across teams than probabilistic scoring, which requires more data than most IT risk programs have on hand.
- Score likelihood and impact from 1 to 5, multiply them, and map the result to a priority band, such as 1 to 6 as low, 8 to 15 as moderate, and 16 to 25 as high.
- Normalize risk categories across teams so that "third party" or "data loss" means the same thing everywhere in the register.
- Map entries to control families, such as those referenced in NIST CSF 2.0, so scores can be aggregated at the enterprise level.
- Apply a materiality threshold: only risks with enterprise-level business impact belong in the strategic register; operational issues stay in team-level trackers.
Normalizing categories and consistent scoring is what allows individual system-level entries to roll up into a single enterprise risk profile, according to NIST's guidance on integrating cybersecurity and enterprise risk management. Without that consistency, aggregation produces a list, not a profile leadership can act on.
Notional examples: sample register rows to copy and adapt
These examples show how business-language phrasing, scoring, and ownership come together in practice. Adapt the wording and thresholds to your organization's size; a small business might combine several of these into one entry, while an enterprise may split each by business unit.
- Access control: shared admin credentials on core financial systems could allow unauthorized fund transfers. Inherent high, residual moderate after MFA rollout. Owner: IT security manager. Treatment: mitigate.
- Cloud misconfiguration: an exposed storage bucket could leak customer records. Inherent high, residual low after access review. Owner: cloud infrastructure lead. Treatment: mitigate.
- Third-party vendor: a payroll processor without SOC 2 attestation could expose employee data. Inherent high, residual moderate pending contract renewal. Owner: procurement director. Treatment: transfer.
- Ransomware: an unpatched remote desktop gateway could allow encryption of production servers. Inherent critical, residual moderate after patching and backups. Owner: infrastructure manager. Treatment: mitigate.
- Data loss: a legacy backup system lacks offsite replication, risking permanent loss of client records. Inherent high, residual high pending upgrade. Owner: operations director. Treatment: mitigate.
- Legacy system failure: an unsupported billing application could halt invoicing for days if it fails. Inherent high, residual moderate with a manual fallback process. Owner: finance systems owner. Treatment: accept, pending replacement budget.
Governance and maintenance: ownership, approvals, and change control
A register earns trust only when every row follows the owner-impact-decision rule: a named business owner, a stated business impact, and a documented treatment decision with a sign-off. A row missing any of the three is not a strategic risk entry, it is a task on a list.
- Review the full enterprise register quarterly and the top-ranked risks monthly.
- Version each update and keep a change log noting what moved, why, and who approved it.
- Build a short leadership reporting pack that highlights new risks, closed risks, and any residual score exceeding appetite.
- Escalate immediately when a residual score crosses the appetite threshold rather than waiting for the next scheduled review.
Pro Tip: Treat the change log as part of the audit trail. Reviewers and auditors often ask not just what the current score is, but how and when it changed.
Secure Techies case study: a real-world register in practice
A financial services risk assessment engagement run by Secure Techies used this same structure: material IT risks were logged in business terms, scored for inherent and residual exposure, and assigned named owners with recorded treatment decisions. That engagement informed the field list and process sequence described above, particularly the emphasis on business-impact phrasing over technical detail.
Integration with asset inventory and configuration management
A risk register disconnected from your asset inventory quickly becomes inaccurate, since risks attach to specific servers, applications, and data stores that change constantly. Linking each register entry to an asset ID in your CMDB or inventory system keeps the risk tied to something real rather than a vague category.
When an asset is decommissioned, its linked risks should close or transfer automatically instead of lingering as stale entries. When a new server or application is provisioned, your intake process should check whether it introduces a new risk category, such as a new vendor dependency or an unpatched software stack.
This integration also supports scoring accuracy. A risk tied to a single low-value workstation scores very differently from the same vulnerability on a domain controller or a system holding regulated data. Without an asset link, likelihood and impact estimates become guesswork rather than grounded assessments.
For teams running a formal configuration management database, tag each CMDB record with any open risk IDs, and reverse the link in the register so each entry lists its associated asset or asset group. This two-way mapping makes it possible to answer a question that often comes up during audits or incident response: which risks apply to this specific system right now. It also flags risk concentration, showing when too many high-severity risks cluster on a single critical asset, which itself becomes a governance signal worth escalating.

Linking incidents and root cause analysis to risk updates
An incident is often the clearest evidence that a risk score was wrong. When a security event occurs, the root cause analysis should feed directly back into the register rather than living only in an incident report that nobody revisits.
Start by checking whether the incident maps to an existing risk entry. If a phishing email led to a compromised account, and "credential compromise via phishing" is already logged, update its residual score based on what actually happened rather than what was assumed. If no matching entry exists, that gap itself is a finding: the register missed a real exposure, and a new entry belongs on the list.
Root cause analysis frequently reveals that a control assumed to be effective was not. A firewall rule thought to block a certain traffic pattern, or an endpoint tool assumed to catch a certain malware family, may have failed in practice. That failure should lower the confidence in "existing controls" for every register entry relying on the same control, not just the one tied to the incident.
Build a lightweight habit around this: after every incident review, spend ten minutes checking the register for entries that need a score change, a new control note, or an updated treatment decision. Over several review cycles, this keeps the register grounded in what is actually happening in the environment instead of a static snapshot from the last risk assessment.

Common pitfalls in maintaining an IT risk register
The most common failure is letting the register grow into a list of every technical issue anyone has ever raised. Without a materiality threshold, it stops being strategic and becomes an unmanageable backlog that nobody reviews. Apply the "enterprise-impacting" filter consistently and route lower-level operational issues to team trackers instead.
A second pitfall is missing owners. A risk assigned to "IT" or left blank rarely gets resolved, because no individual is accountable for the decision. Every entry needs a named person, not a department.
Stale entries are another frequent problem. Risks get logged, scored once, and never revisited, even as controls change or new information arrives from audits and incidents. A quarterly review cadence, backed by a change log, keeps scores honest.
Duplication also creeps in over time, especially when different teams log similar risks under slightly different wording. Periodically scan for near-duplicate entries and merge them, keeping the more complete business-impact description.
Finally, registers that stay purely technical lose executive attention. If leadership cannot connect an entry to a business consequence within one sentence, rewrite it before the next reporting cycle.
What the register actually needs to work
Most advice on this topic focuses on templates and scoring matrices, but the field list matters far less than the discipline behind it. A register with ten well-owned, clearly scored risks and honest treatment decisions is more useful than one with two hundred rows nobody has revisited since last year.
The part that gets underrated is the review cadence. Teams spend hours perfecting a scoring model and then let the register sit untouched for six months, which defeats the purpose entirely. A simpler scoring approach reviewed monthly beats a sophisticated one reviewed annually.
The other gap: too many registers stay technical because the people filling them out are technical. Forcing every entry into a one-sentence business consequence is uncomfortable at first, but it is the single change that makes a register useful to people who control budget. Start there before worrying about which control framework to map against.
— Alex
How Secure Techies can help you build and maintain a register
Turning a template into a working risk register takes ongoing effort, and Secure Techies supports that work directly rather than leaving you with a spreadsheet and no follow-through.
- Compliance & Security Audits identify and score material risks as a starting point for your register.
- Cybersecurity Solutions provide the monitoring and endpoint detection that feed residual risk updates.
- Managed IT Services support ongoing remediation tracking so treatment decisions actually get closed out.
If you want help building or maintaining your register, start with a compliance and security audit to establish your baseline.
Sources
FAQ
How do you perform an IT risk assessment?
An IT risk assessment identifies assets, threats, and vulnerabilities, then estimates likelihood and impact using a structured process. NIST SP 800-30 describes this as four stages: prepare, conduct, communicate, and maintain. The results feed directly into your risk register as inherent and residual scores.
What is a risk register?
A risk register is a structured repository that lists an organization's material risks along with their description, impact, likelihood, owner, and treatment decision. NIST IR 8286 frames the cybersecurity version as a tool that rolls system-level risks up into enterprise risk management for leadership decisions.
How do I create a risk register?
Start by scoping which systems or business units the register covers, then populate a template with fields for description, category, likelihood, impact, owner, and treatment decision. Score each entry, assign a named owner, and set a review cadence so the register stays current rather than becoming a one-time document.
What is a risk in IT security?
An IT security risk is the potential for a threat to exploit a vulnerability in a system, application, or process, causing harm to operations, data, or reputation. It is typically expressed as a combination of likelihood and impact, which together determine how much attention and budget it deserves relative to other risks on the register.